NewsVulnerability
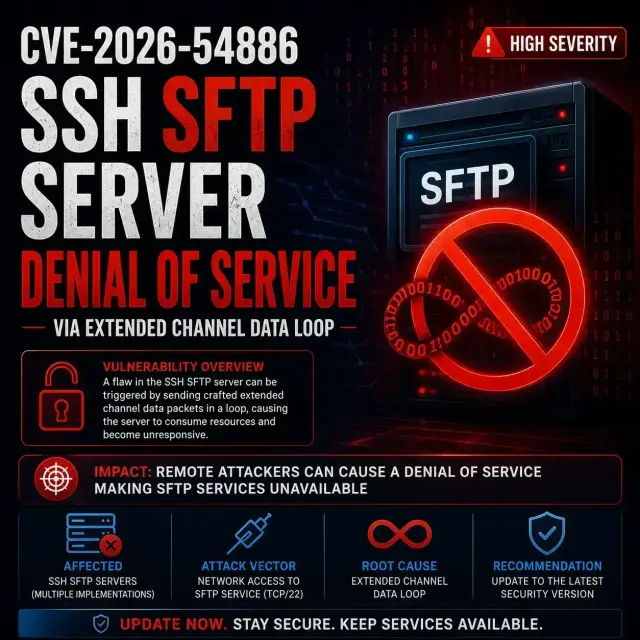
CVE-2026-54886: SSH SFTP Server Denial of Service via Extended Channel Data Loop
A newly disclosed vulnerability, tracked as CVE-2026-54886, can trigger a denial-of-service condition in an affected SSH/SFTP server implementation through an infinite loop in the handling of extended channel data. Administrators should watch for vendor advisories and patch details as they become available.