

11 of 100 stories tagged “Patch Management”
More 129
Microsoft confirms KB5120998 resets Windows 11 desktop settings
Microsoft has confirmed that the optional KB5120998 preview update stops some Windows 11 desktop settings from loading, leaving a solid black background that users cannot restore manually.
Microsoft Delays Exchange SE CU1 Again, Cites AI-Found Security Bugs
Microsoft has delayed Exchange Server Subscription Edition Cumulative Update 1 for a second time, saying engineers cannot keep pace with the volume of vulnerabilities surfaced by AI-assisted code scanning. The company has not given a new release window.

Microsoft Patches Dozen-Plus Flaws, Apple Fixes Screen Sharing Bug CVE-2026-65400
Microsoft patched more than a dozen vulnerabilities across Active Directory, Azure, Entra, SharePoint and Teams, including three CVSS 10/10 flaws. Apple fixed a single Screen Sharing authentication bypass (CVE-2026-65400) in macOS.
wp2shell: WordPress Core Pre-Auth RCE Fixed in 6.9.5 and 7.0.2
WordPress shipped forced updates 6.9.5 and 7.0.2 on July 17, 2026, closing a pre-auth remote code execution flaw named wp2shell that an anonymous HTTP request can trigger against a default core install with no plugins. The bug affects 6.9.0-6.9.4 and 7.0.0-7.0.1.

Certighost CVE-2026-54121: Public Exploit Turns a Domain User Into a Domain Controller
Researchers H0j3n and Aniq Fakhrul have released a working exploit for Certighost, an Active Directory Certificate Services flaw patched in July 2026 that let any low-privileged domain user impersonate a domain controller and reach full domain compromise.
BeyondTrust Publishes Security Advisories for Privileged Access Products
BeyondTrust runs a public security advisory page covering vulnerabilities across its Privileged Remote Access, Remote Support, and Privileged Identity products. If you run these tools as an IT team or MSP, track the advisories and apply fixes fast. BeyondTrust products have a history of actively exploited flaws.
BeyondTrust Patches Critical Auth Bypass Vulnerability in Remote Support and PRA
BeyondTrust has patched a critical auth bypass vulnerability set in Remote Support (RS) and Privileged Remote Access (PRA). Two of the four flaws are critical pre-authentication bypasses (CVE-2026-40138 and CVE-2026-40139, CVSS 9.2). Under a specific authentication configuration, they let unauthenticated attackers reach affected appliances.
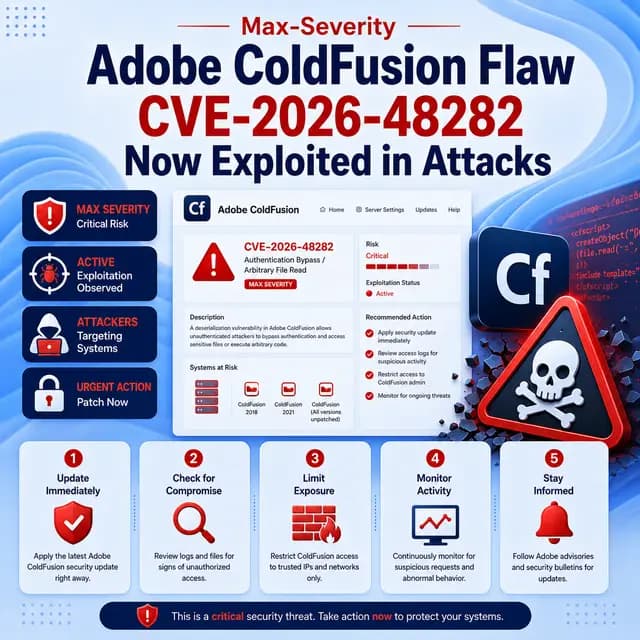
Max-Severity Adobe ColdFusion Flaw CVE-2026-48282 Now Exploited in Attacks
Canada's Cyber Centre warns that attackers are exploiting CVE-2026-48282, a maximum-severity Adobe ColdFusion vulnerability that allows unauthenticated remote code execution. Adobe patched the flaw days earlier and urged admins to update within 72 hours.
Google Patches 382 Chrome Vulnerabilities, 15 Rated Critical
Google's latest Chrome Stable channel update fixes 382 security flaws, including 15 critical-severity issues, with no in-the-wild exploitation reported. Most were found internally by Google.
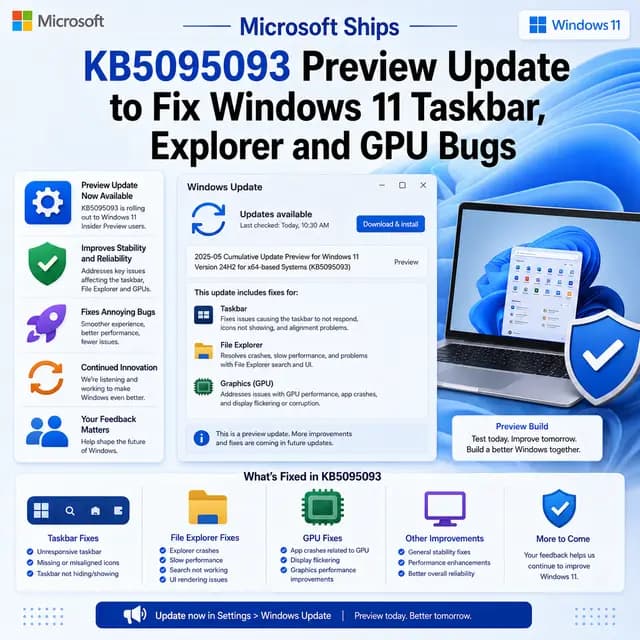
Microsoft Ships KB5095093 Preview Update to Fix Windows 11 Taskbar, Explorer and GPU Bugs
Microsoft released KB5095093, the June 23, 2026 optional preview cumulative update for Windows 11, advancing systems to OS Builds 26200.8737 and 26100.8737. The non-security update fixes eight reliability defects including taskbar input failures, File Explorer refresh bugs, DirectX rendering crashes and Bluetooth audio disconnects, but ships with three known installation issues.
Microsoft Ships KB5087054 .NET Framework Update for Windows 11 24H2, Patching Two CVEs
Microsoft released KB5087054, a cumulative security update for .NET Framework 3.5 and 4.8.1 on Windows 11 Version 24H2 (x64). The update patches an elevation-of-privilege flaw in the CLR (CVE-2026-0234) and an ASP.NET request-validation bypass (CVE-2026-0235), alongside garbage-collector and reliability fixes. It requires a restart and carries several known post-install issues admins should test for.