

6 of 100 stories tagged “Vulnerability Management”
More 129
Microsoft's August 2026 Patch Tuesday Fixes About 400 Flaws and 3 Zero-Days
Microsoft's August 2026 Patch Tuesday addresses roughly 400 vulnerabilities, including 42 rated Critical and three zero-days. One, CVE-2026-68820, is already exploited in the wild and now sits in CISA's KEV catalog.
PaperCut Patches Actively Exploited PaperCut NG/MF Zero-Day Chain
PaperCut has shipped emergency patches for an actively exploited authentication-bypass and remote-code-execution chain in PaperCut NG and MF, now tracked as CVE-2026-81578 and CVE-2026-82078, after confirming customer incidents tied to the flaws.
CVE-2026-62873: Critical Microsoft 365 Admin Center EoP Flaw Patched
Microsoft patched CVE-2026-62873, a critical elevation-of-privilege flaw in Microsoft 365 Admin Center caused by improper cryptographic signature verification, as part of its August 2026 Patch Tuesday release covering 421 CVEs.
BeyondTrust Publishes Security Advisories for Privileged Access Products
BeyondTrust runs a public security advisory page covering vulnerabilities across its Privileged Remote Access, Remote Support, and Privileged Identity products. If you run these tools as an IT team or MSP, track the advisories and apply fixes fast. BeyondTrust products have a history of actively exploited flaws.
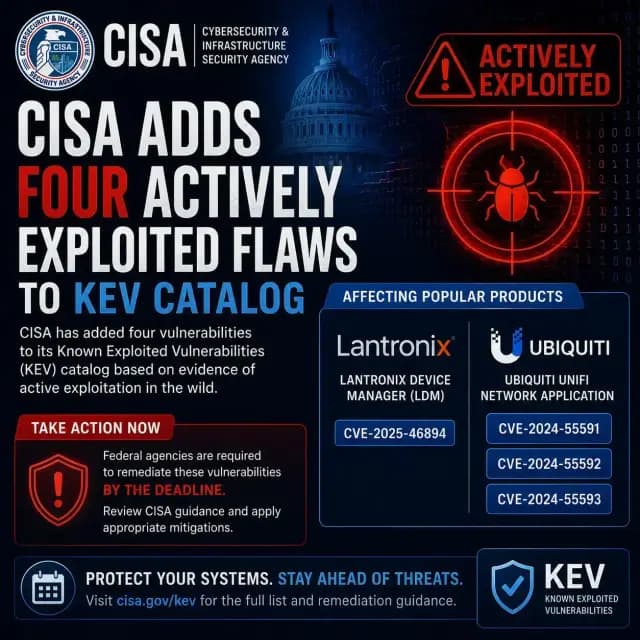
CISA Adds Four Actively Exploited Flaws to KEV Catalog: Lantronix, Ubiquiti UniFi
CISA has added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog based on evidence of active exploitation: one affecting Lantronix EDS5000 device servers and three in Ubiquiti UniFi OS. Federal civilian agencies must remediate under BOD 26-04, and CISA urges all organizations to prioritize these fixes.

Microsoft Ships KB5094126 June 2026 Security Update for Windows 11 24H2 and 25H2
Microsoft released KB5094126 on June 9, 2026, a security update for Windows 11 versions 24H2 and 25H2 and Windows Server 2025. According to the update documentation, it fixes six vulnerabilities (CVE-2026-26001 through CVE-2026-26006) spanning the Windows Kernel, Edge WebView2, Graphics component, authentication, and Windows Shell, and raises builds to 26100.8655 (24H2) and 26200.8655 (25H2).