

CISA: Medusa Ransomware Has Hit Over 500 Critical Infrastructure Orgs
A joint federal advisory updates last year's Medusa warning, showing the ransomware-as-a-service gang's victim count grew by more than 60% in about a year.

On this page
Key takeaways
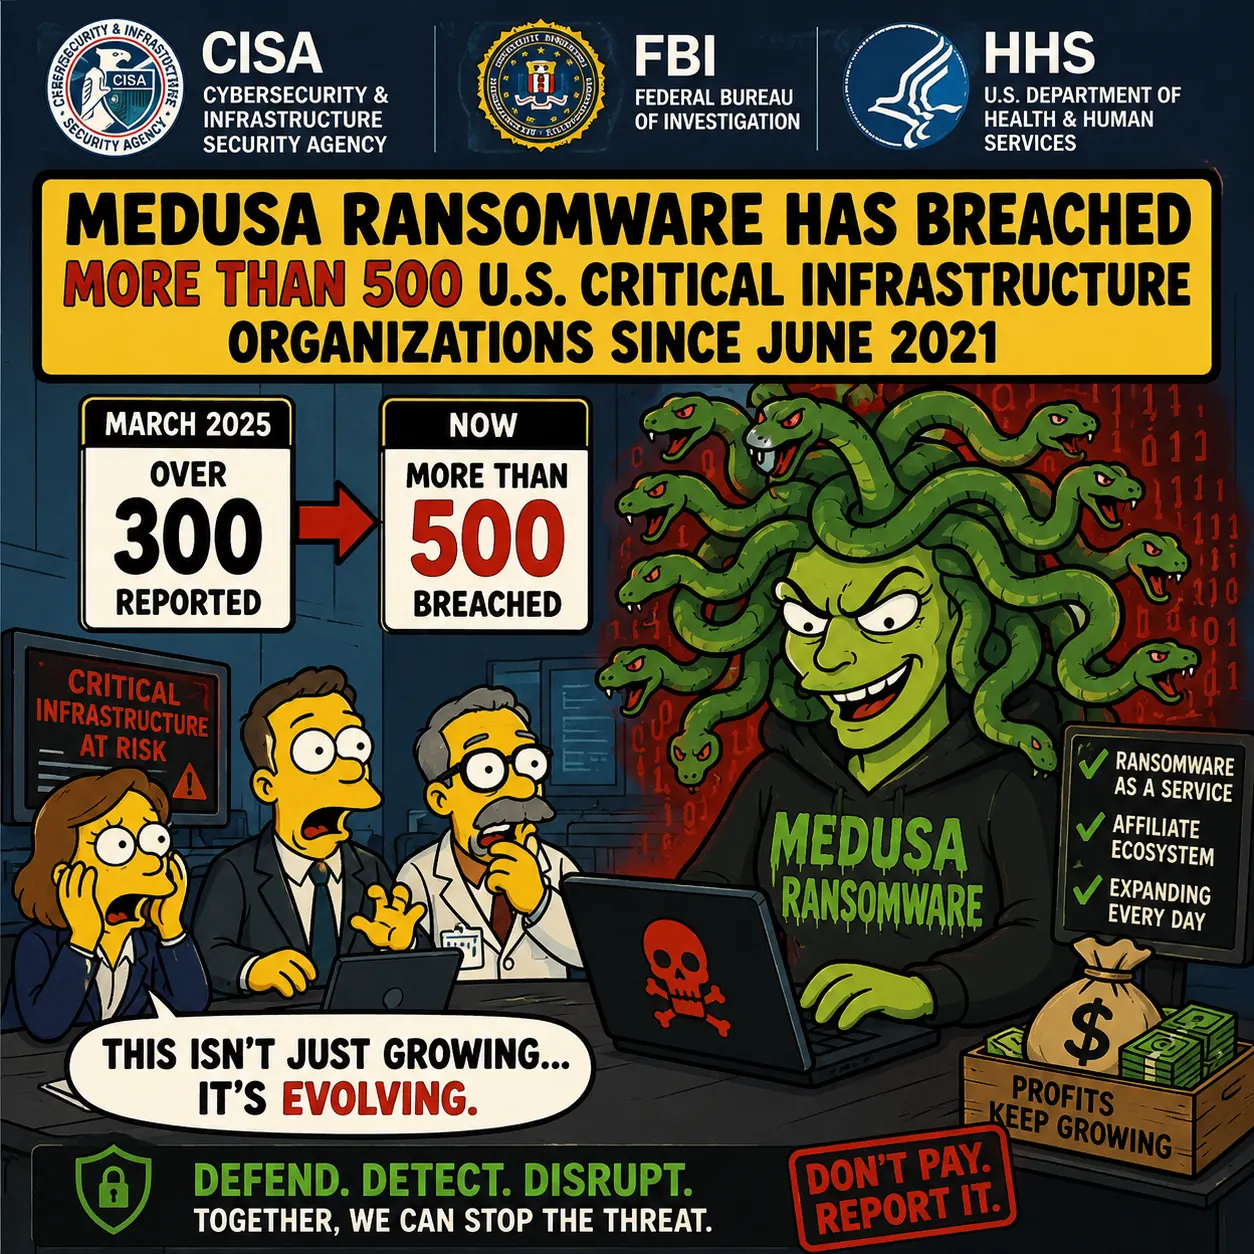
- CISA, the FBI and HHS say Medusa has impacted over 500 critical infrastructure organizations as of April 2026, up from over 300 in March 2025.
- Medusa surfaced in January 2021 but only gained momentum after launching its Medusa Blog leak site in 2023.
- The group operates as ransomware-as-a-service, paying initial access brokers between $100 and $1 million for entry into victim networks.
- Hardest-hit sectors include Healthcare and Public Health, Defense Industrial Base, Government Services and Facilities, and Financial Services.
- Agencies recommend patching known vulnerabilities, segmenting networks and blocking untrusted access to internal remote services.
What to do now
High urgency- Patch known exploited vulnerabilities in operating systems, software and firmware promptly
- Segment networks to limit lateral movement after an initial compromise
- Block untrusted external access to internal remote services
- Monitor for known Medusa indicators, including Ligolo-ng, Nezha, MeshAgent and unauthorized remote access tools
- Review use of legitimate remote management tools like AnyDesk, Atera and SimpleHelp for unauthorized instances
CISA said Tuesday, in a joint advisory with the FBI and the Department of Health and Human Services, that the Medusa ransomware gang has breached more than 500 U.S. critical infrastructure organizations as of April 2026, though reports differ on when the operation began, with some pointing to January 2021 and others to June 2021. The update revises an earlier joint report from March 2025 that put the toll at over 300 victims, marking a sharp rise in roughly a year.
Medusa has grown from a closed ransomware crew into a ransomware-as-a-service operation that recruits initial access brokers and pressures victims through a public leak site, and its expanding footprint across healthcare, government and defense targets underscores why federal agencies keep updating defenders on its tactics.
CISA, the FBI and HHS say Medusa ransomware has breached over 500 U.S. critical infrastructure organizations since 2021, up from over 300 reported in March 2025.
A joint federal advisory update shows Medusa ransomware's victim count grew from over 300 to over 500 critical infrastructure organizations in about a year, driven by an affiliate-based ransomware-as-a-service model.
Affected & context
CISA, the FBI and HHS issued a joint advisory update stating Medusa ransomware has impacted more than 500 U.S. critical infrastructure organizations as of April 2026, compared with over 300 in a March 2025 advisory.
Medusa's affiliate-driven ransomware-as-a-service model has kept expanding into healthcare, government and defense-sector networks, and the agencies say the group moves fast to exploit newly disclosed vulnerabilities before patches land.
U.S. organizations in Healthcare and Public Health, Defense Industrial Base, Critical Manufacturing, Government Services and Facilities, Information Technology, Financial Services, plus medical, education, legal, insurance and manufacturing sectors.
- Threat actors
- Medusa ransomware gang
- Malware
- Medusa ransomware
- Geography
- United States
- Industry
- Healthcare and Public HealthDefense Industrial BaseCritical ManufacturingGovernment Services and FacilitiesInformation TechnologyFinancial ServicesEducationLegalInsurance
What did the CISA Medusa ransomware advisory say?
CISA, in coordination with the FBI and HHS, published an updated joint advisory stating that Medusa ransomware actors have impacted more than 500 victims across U.S. critical infrastructure sectors as of April 2026. The agencies named Healthcare and Public Health, Defense Industrial Base, Critical Manufacturing, Government Services and Facilities, Information Technology, and Financial Services as the hardest-hit categories, alongside victims in the medical, education, legal, insurance, technology, and manufacturing industries.
This is an update to a prior joint report from March 2025, which had put Medusa's confirmed toll at over 300 critical infrastructure organizations. The roughly 60% jump in reported victims over about a year signals that the group's affiliate network has kept recruiting and operating largely unchecked, according to the advisory.
How Medusa ransomware evolved into a RaaS operation
Medusa ransomware first surfaced in January 2021, according to the advisory, but its activity did not accelerate until 2023, when the group launched its Medusa Blog leak site and began using stolen data as extortion leverage. The operation gained wider media attention in March 2023 after claiming an attack on the Minneapolis Public Schools district and publishing a video of stolen data, per BleepingComputer's reporting.
Medusa began as a closed ransomware variant fully controlled by its developers, then evolved into a ransomware-as-a-service model with an affiliate program. The advisory states that Medusa developers recruit initial access brokers on cybercriminal forums and marketplaces, offering them between $100 and $1 million for gaining entry into victim networks, with an option to work exclusively for Medusa.
Which tools and techniques does Medusa use?
According to CPO Magazine's summary of the advisory, Medusa opportunistically targets organizations with unpatched vulnerabilities rather than picking specific victims, and the group reportedly moves fast to exploit newly disclosed flaws, in some cases before patches become available. The advisory lists updated tactics, techniques and procedures along with indicators of compromise for defenders.
- Uses Interactsh URLs to confirm successful exploitation attempts.
- Applies PowerShell obfuscation and deletes command history to hide activity.
- Hides payloads in folders excluded from active Windows Defender scanning.
- Uses Ligolo-ng for tunneling and pivoting between compromised networks and attacker infrastructure.
- Uses Mimikatz to harvest credentials after disabling security tools, plus legitimate remote access tools such as AnyDesk, Atera, ConnectWise and SimpleHelp.
Who is affected by Medusa's ransomware-as-a-service model?
The advisory identifies Healthcare and Public Health, Defense Industrial Base, Critical Manufacturing, Government Services and Facilities, Information Technology, and Financial Services as the primary sectors hit, with additional victims in medical, education, legal, insurance, technology and manufacturing organizations. Security researcher John Strand, owner of Black Hills Information Security, told CPO Magazine that ransomware groups' continued focus on healthcare and critical infrastructure creates pressure that extends beyond the direct financial impact on any single victim organization.
Because Medusa is a common name in the malware world, the advisory also flags a risk of confusion: separate operations named Medusa exist as a Mirai-based botnet with ransomware features and as an Android malware-as-a-service tool also tracked as TangleBot. Reporting on Medusa ransomware has also been mixed up at times with the unrelated MedusaLocker operation, according to BleepingComputer.
What should network defenders do now?
CISA, the FBI and HHS recommend that network defenders mitigate known security vulnerabilities across operating systems, software and firmware to close off the exploitation paths Medusa relies on for initial access. The agencies also advise segmenting networks to limit lateral movement after any single system is compromised.
- Patch known vulnerabilities promptly, since Medusa affiliates opportunistically target unpatched systems.
- Segment networks to block lateral movement following an initial compromise.
- Block access from untrusted origins to remote services exposed on internal systems.
- Review the advisory's listed indicators of compromise and TTPs for threat hunting.
Why does the growth in Medusa's victim count matter?
The jump from over 300 to over 500 reported critical infrastructure victims in roughly a year shows Medusa's affiliate-based business model is still attracting initial access brokers willing to sell entry into corporate and government networks. Because CISA counts victims across sectors that include hospitals, financial institutions and defense contractors, each new intrusion carries potential consequences well beyond the breached organization itself, from disrupted patient care to compromised sensitive data.
The advisory's emphasis on fast exploitation of newly disclosed vulnerabilities, sometimes ahead of available patches, adds pressure on IT and security teams already working through routine patch cycles. MSPs and internal IT teams managing critical infrastructure clients should treat the updated victim count as a signal to revisit patch prioritization and remote-access exposure rather than a one-time news item.
Impact
Medusa's growth to over 500 confirmed victims shows a ransomware-as-a-service crew can outrun patch cycles across healthcare, government and defense networks.
Business impact
Victims face double-extortion pressure: Medusa lists organizations on its leak site with payment countdowns and contacts them within 48 hours, offering discounts for fast payment or threatening to sell stolen data.
Technical impact
Affiliates gain initial access via brokers, then use tools including Ligolo-ng, Nezha, MeshAgent, webshells and legitimate remote access software such as AnyDesk, Atera, ConnectWise, SimpleHelp and others to move laterally and exfiltrate data.
Security impact
CISA, the FBI and HHS say Medusa does not develop its own zero-days but moves quickly to exploit recently disclosed vulnerabilities, and uses Mimikatz plus PowerShell obfuscation after disabling security tools; CPO Magazine reported that the advisory found Medusa has in some cases exploited vulnerabilities up to two weeks before patches were available.
Privacy impact
Double-extortion tactics mean stolen victim data, including from healthcare and government networks, can be published or sold if ransoms go unpaid.
Affected audience: IT and security teams at critical infrastructure organizations, Healthcare and Public Health sector administrators, Defense Industrial Base and government IT staff, Managed service providers supporting remote access tools
Action required.
Technical details
- Exploitation
- Exploited in the wild
- Attack vector
- Initial access purchased from brokers, followed by exploitation of recently disclosed, sometimes unpatched vulnerabilities in internet-facing systems.
Indicators of compromise
- Other
Interactsh URLsUsed by Medusa actors to confirm successful exploitation of vulnerabilities
Source: CISA/FBI/HHS joint advisory
Confidence: Medium
- Other
Ligolo-ngTunneling and pivoting tool used to link compromised networks to attacker infrastructure
Source: CISA/FBI/HHS joint advisory
Confidence: Medium
- Other
NezhaOpen-source remote management tool used to maintain visibility into compromised systems
Source: CISA/FBI/HHS joint advisory
Confidence: Medium
- Other
MeshAgentUsed to remotely control compromised computers
Source: CISA/FBI/HHS joint advisory
Confidence: Medium
Detection methods
- Monitor for webshells and unauthorized remote access tools including AnyDesk, Atera, BeyondTrust, ConnectWise, eHorus, N-able, SimpleHelp and Splashtop
- Look for PowerShell obfuscation and deleted command history consistent with anti-forensic behavior
- Check payload storage locations excluded from Windows Defender active scanning
Mitigations
- Mitigate known security vulnerabilities in operating systems, software and firmware to prevent exploitation
- Segment networks to block lateral movement after compromise
- Block access from untrusted origins to remote services on internal systems
Technical references
Response
Authorities
CISA, the FBI and HHS said in the joint advisory that as of April 2026, Medusa actors have impacted more than 500 victims across multiple critical infrastructure sectors, including Healthcare and Public Health, Defense Industrial Base, Critical Manufacturing, Government Services and Facilities, Information Technology and Financial Services.
Customer guidance
The agencies recommend patching known vulnerabilities in operating systems, software and firmware, segmenting networks to limit lateral movement, and blocking untrusted external access to internal remote services.
Response status: Acknowledged
Patch available: No
Workaround available: No
Updates
Victim count raised to over 500
Major updateJoint CISA/FBI/HHS advisory revised the March 2025 estimate of over 300 victims upward to more than 500 as of April 2026.
FAQ
How many organizations has Medusa ransomware hit?
CISA, the FBI and HHS say Medusa has impacted more than 500 U.S. critical infrastructure organizations as of April 2026, up from over 300 reported in a March 2025 advisory.
When did Medusa ransomware first appear?
The Medusa ransomware operation surfaced in January 2021, according to the joint advisory, though other reporting places initial detection around June 2021; its activity picked up after it launched the Medusa Blog leak site in 2023.
How does Medusa gain initial access to victim networks?
Medusa developers recruit initial access brokers on cybercriminal forums and marketplaces, paying them between $100 and $1 million and offering some the chance to work exclusively for the operation.
Is Medusa the same as MedusaLocker?
No. CISA notes that Medusa is a distinct operation from MedusaLocker, though the similar names have caused confusion in reporting.
Which sectors has Medusa targeted most?
The advisory lists Healthcare and Public Health, Defense Industrial Base, Critical Manufacturing, Government Services and Facilities, Information Technology and Financial Services as hardest hit, along with medical, education, legal, insurance and manufacturing organizations.
What should defenders do to reduce Medusa risk?
CISA, the FBI and HHS recommend patching known vulnerabilities quickly, segmenting networks to block lateral movement, and blocking untrusted access to internal remote services.
The bottom line
A joint CISA, FBI and HHS advisory update shows Medusa ransomware's confirmed U.S. critical infrastructure victim count grew from over 300 in March 2025 to over 500 by April 2026.
Medusa's shift to an affiliate-driven ransomware-as-a-service model has let it outpace patch cycles and expand rapidly across healthcare, government and defense networks.
What happens next
Defenders should expect continued affiliate recruitment and fast exploitation of newly disclosed vulnerabilities as Medusa's ransomware-as-a-service model keeps scaling.
Related articles: Microsoft Ships KB5094128 for Windows Server 2022, Patching Four Critical Flaws · CVE-2026-62873: Critical Microsoft 365 Admin Center EoP Flaw Patched · CISA: SharePoint RCE Flaw CVE-2026-45659 Now Actively Exploited · Cruciferra Crypter: How a $450-a-Month Service Hides RATs From EDR · fairlife Ransomware Attack: Coca-Cola Confirms Data Theft as US Production Resta · Microsoft Ships KB5082198 for Windows Server 2016 and Windows 10 1607, Fixing Fo.
What to do
Review the joint advisory's indicators of compromise and prioritize patching, network segmentation and remote-access controls.
Sources
BleepingComputer · Aug 19, 2026 · Primary source
Claims supported
- Medusa has impacted more than 500 critical infrastructure organizations since June 2021
- CISA, FBI and HHS issued the joint advisory update
- Medusa surfaced in January 2021 and grew after launching its leak site in 2023
- Medusa pays initial access brokers between $100 and $1 million
CPO Magazine · Aug 19, 2026
Claims supported
- Medusa uses tools including Ligolo-ng, Nezha, MeshAgent, webshells and remote access software
- Medusa exploits vulnerabilities sometimes two weeks before patches are available
- Expert commentary from John Strand of Black Hills Information Security
Slashdot · Aug 19, 2026
Claims supported
- Medusa victim count rose from over 300 to over 500 since 2021