

5 of 50 explainers tagged “Windows Server”
More 154
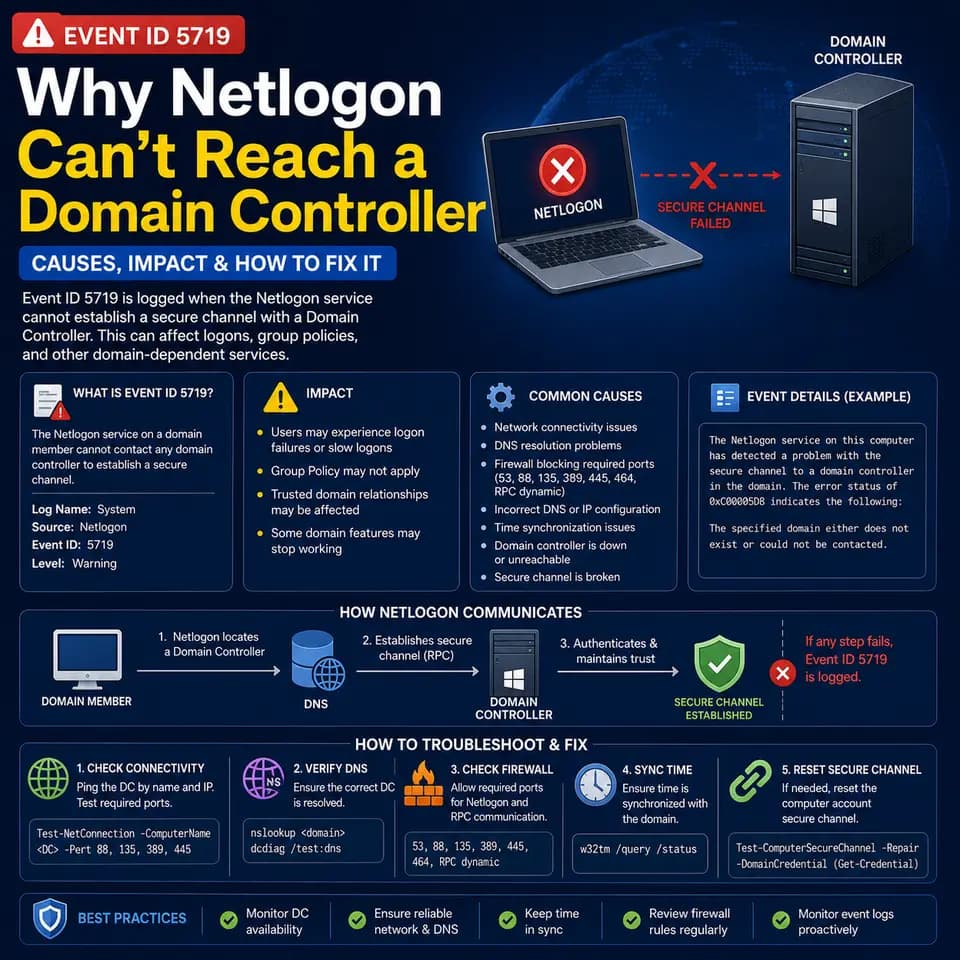
Event ID 5719: Why Netlogon Can't Reach a Domain Controller
Event ID 5719 is a Netlogon warning logged when a domain-joined Windows computer fails to establish a secure session with a domain controller. Common causes include network timing at boot, DNS misconfiguration, and broken secure channel trust.

Windows Event ID 1074 (User32): System Restart or Shutdown Initiated
Windows Event ID 1074 from User32 records who or what cleanly initiated a restart or shutdown: the process, account, reason code, and shutdown type. Learn what it means, how to read the reason code, and how it differs from crash events.
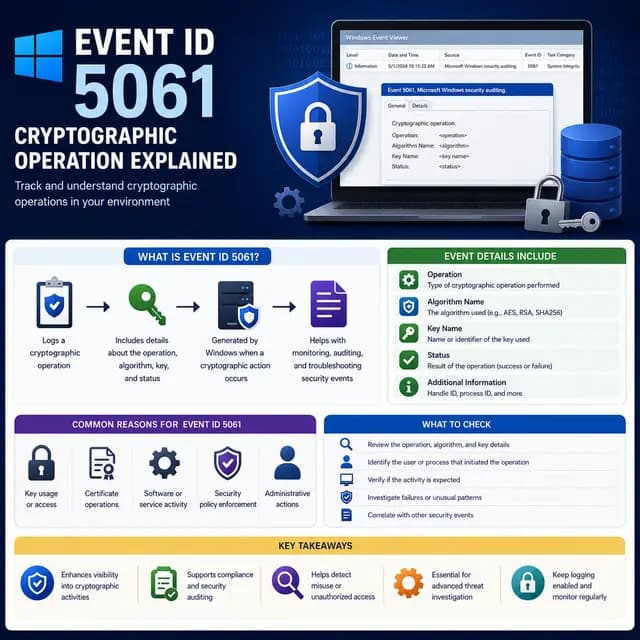
Event ID 5061: Cryptographic Operation Explained
Event ID 5061 is a Windows security audit event that logs cryptographic operations performed through a Key Storage Provider. This explainer covers what triggers it, how to read its fields, the common 0x80090016 failure, and when it signals a real security concern.
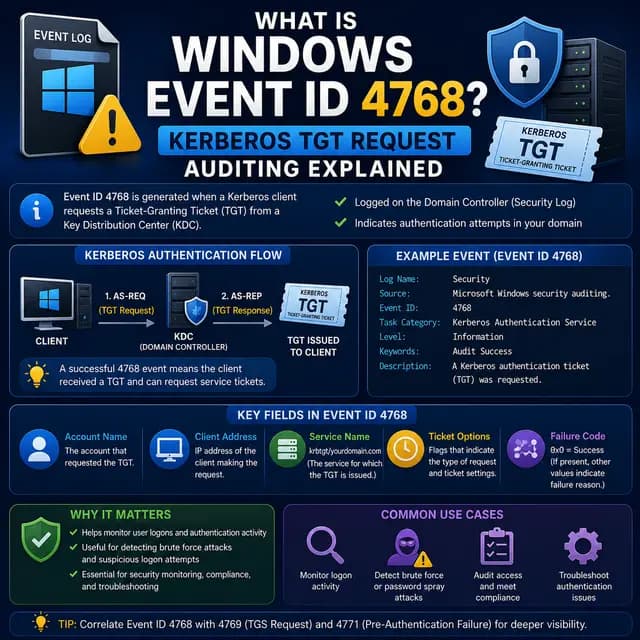
What Is Windows Event ID 4768? Kerberos TGT Request Auditing Explained
Windows Event ID 4768 logs every Kerberos TGT request on domain controllers. This explainer covers what it means, how the Kerberos AS-REQ flow works, key result codes, and how to use 4768 for security monitoring.
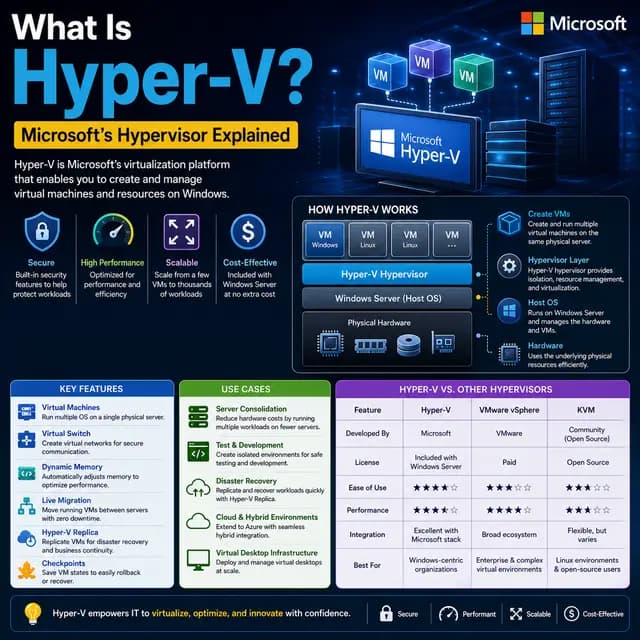
What Is Hyper-V? Microsoft's Hypervisor Explained
Hyper-V is Microsoft's native Type 1 (bare-metal) hypervisor for creating and running virtual machines on x64 Windows systems. Learn how it works, its architecture, how it's licensed today, and where it fits.