

4 of 50 explainers tagged “Windows Security”
More 154
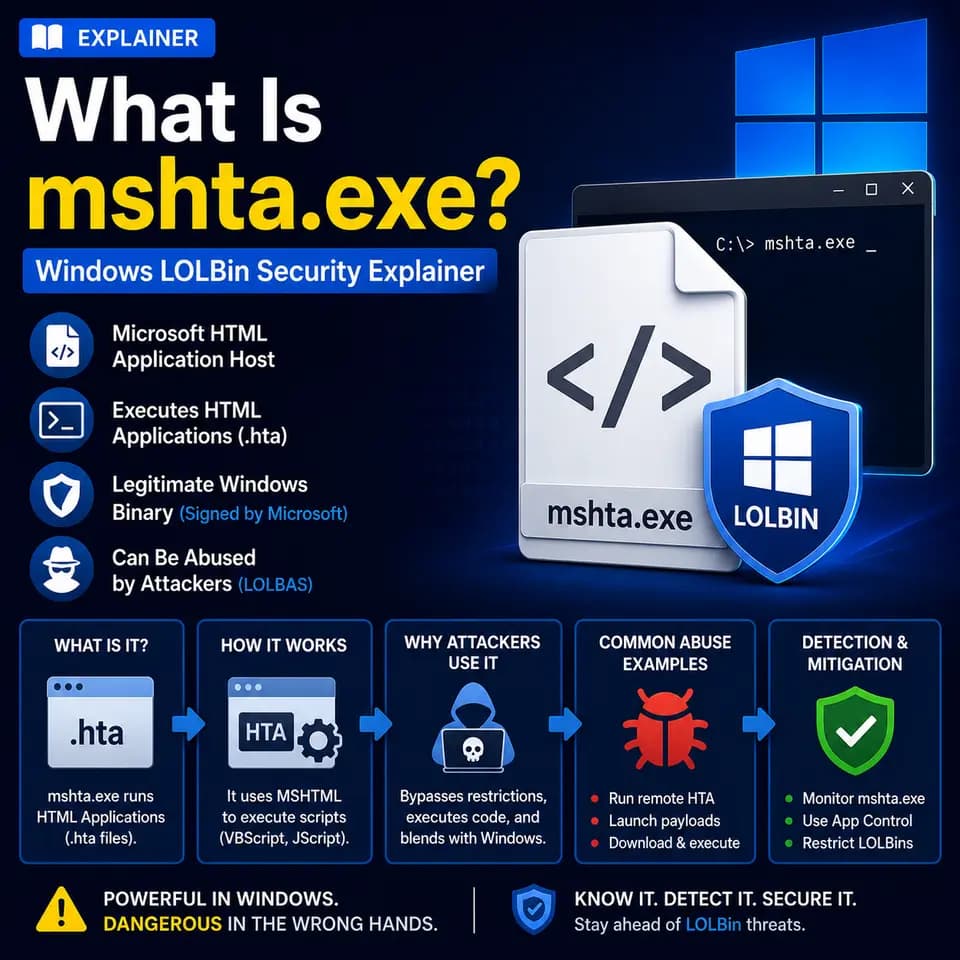
What Is mshta.exe? Windows LOLBin Security Explainer
mshta.exe is a Windows binary for running HTA files. Per MITRE ATT&CK T1218.005, attackers abuse it as a LOLBin to execute malicious VBScript/JScript, bypass AppLocker, and proxy payload execution. Covers detection, blocking, and defense strategies.
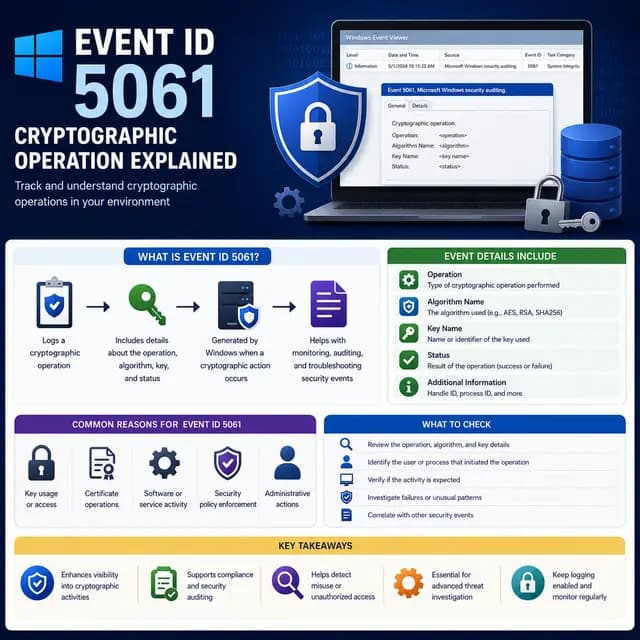
Event ID 5061: Cryptographic Operation Explained
Event ID 5061 is a Windows security audit event that logs cryptographic operations performed through a Key Storage Provider. This explainer covers what triggers it, how to read its fields, the common 0x80090016 failure, and when it signals a real security concern.
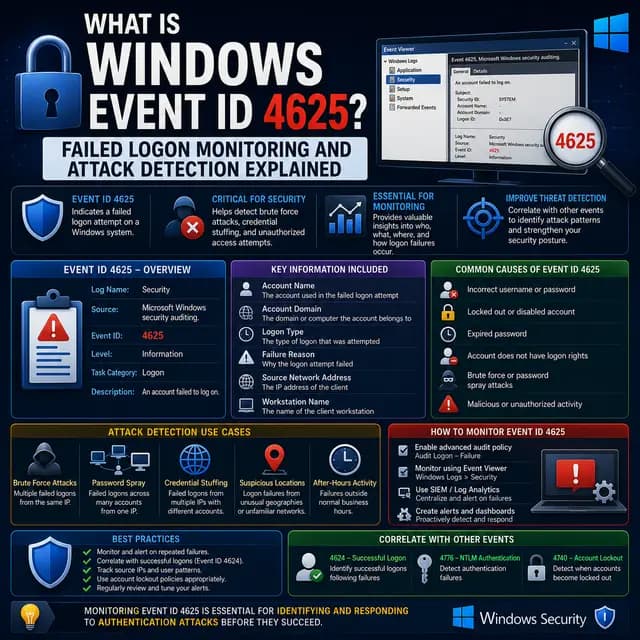
What Is Windows Event ID 4625? Failed Logon Monitoring and Attack Detection Explained
Windows Event ID 4625 logs every failed logon attempt. This explainer covers Sub Status codes, Logon Types, brute-force detection patterns, audit policy setup, and PowerShell analysis techniques.
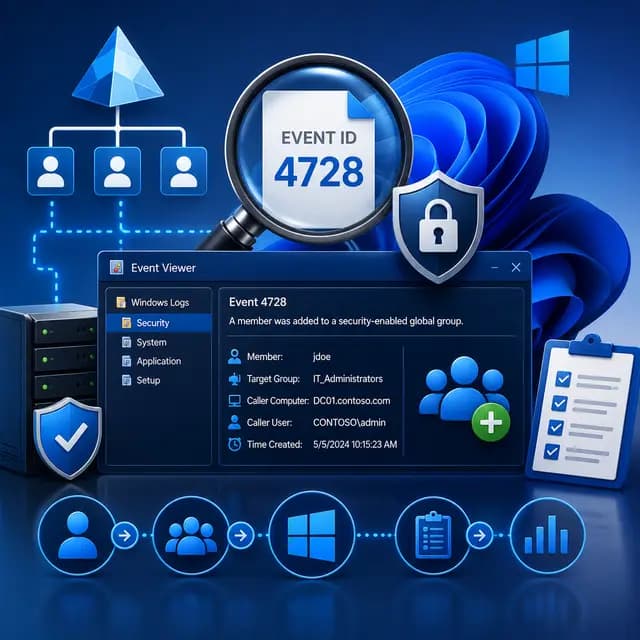
What Is Windows Event ID 4728? Active Directory Group Membership Auditing Explained
Windows Event ID 4728 logs every time a member is added to a security-enabled global group in Active Directory. This explainer covers what the event means, how it works, why it matters for security teams, and how to monitor it effectively.