

5 of 50 explainers tagged “Active Directory”
More 154
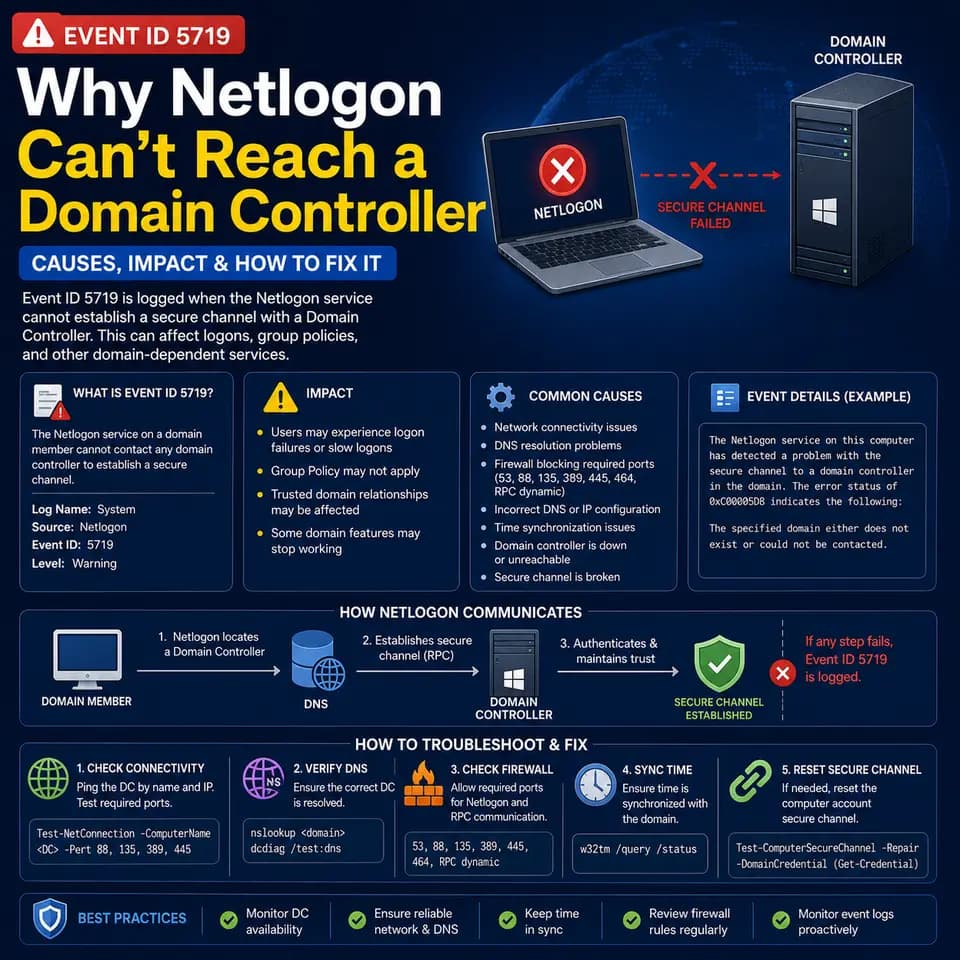
Event ID 5719: Why Netlogon Can't Reach a Domain Controller
Event ID 5719 is a Netlogon warning logged when a domain-joined Windows computer fails to establish a secure session with a domain controller. Common causes include network timing at boot, DNS misconfiguration, and broken secure channel trust.

What Is LDAP? Lightweight Directory Access Protocol Explained
LDAP is the standard protocol for querying and modifying directory services like Active Directory. It runs on port 389 (plaintext) or 636 (TLS). This explainer covers LDAP operations, Active Directory integration, LDAPS, and security best practices.
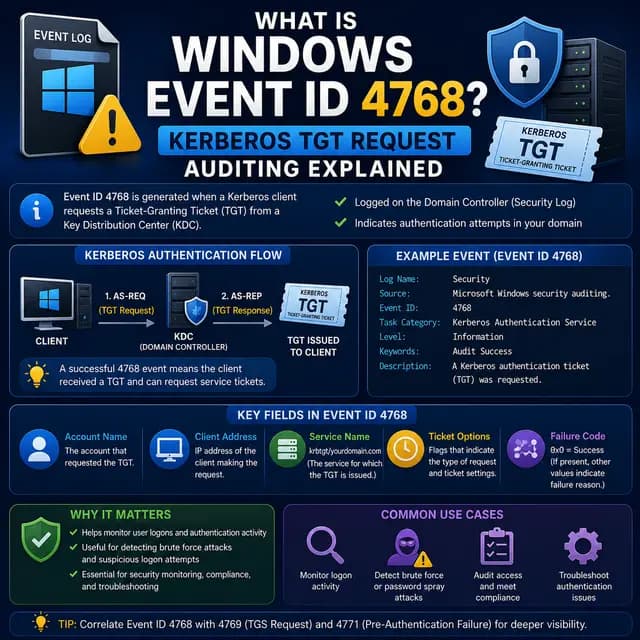
What Is Windows Event ID 4768? Kerberos TGT Request Auditing Explained
Windows Event ID 4768 logs every Kerberos TGT request on domain controllers. This explainer covers what it means, how the Kerberos AS-REQ flow works, key result codes, and how to use 4768 for security monitoring.
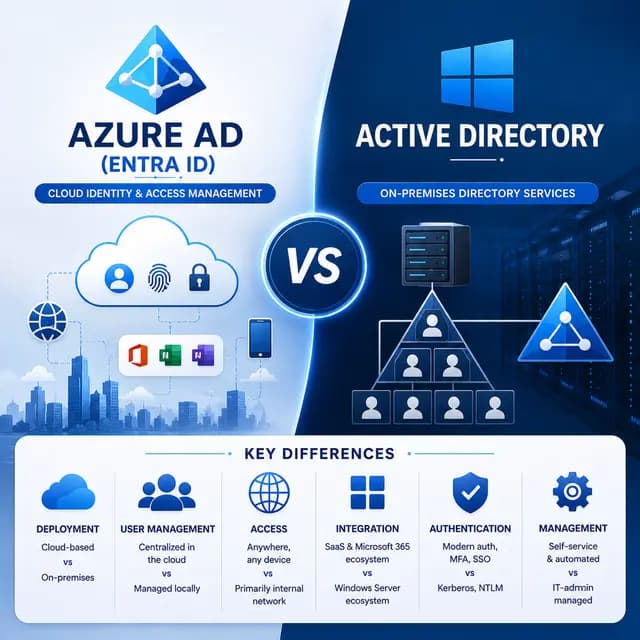
Azure AD vs Active Directory (Entra ID): Key Differences Explained
Active Directory and Microsoft Entra ID (formerly Azure AD) both handle identity, but they were built for different eras. This explainer breaks down their trust models, authentication protocols, and when to use each.
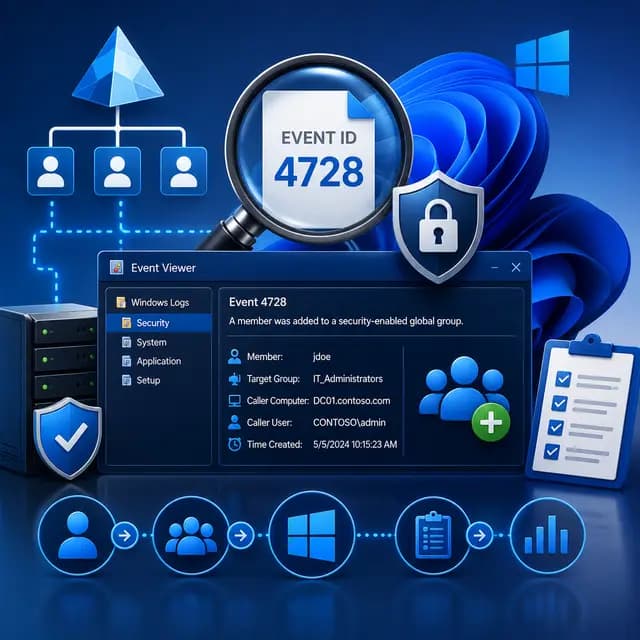
What Is Windows Event ID 4728? Active Directory Group Membership Auditing Explained
Windows Event ID 4728 logs every time a member is added to a security-enabled global group in Active Directory. This explainer covers what the event means, how it works, why it matters for security teams, and how to monitor it effectively.