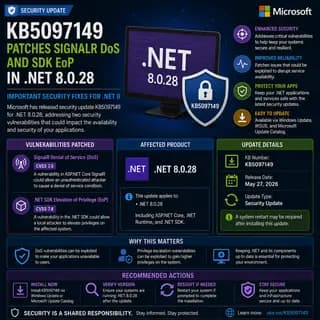
KB5097149 Patches SignalR DoS and SDK EoP in .NET 8.0.28
KB5097149 patches three CVEs in .NET 8.0: serialization RCE, ASP.NET Core DoS, and cryptographic info disclosure. Updates to version 8.0.28 on Windows, Linux, and macOS. No known issues.
Latest updates on cloud, security, Microsoft and the tools that keep your infrastructure running.
Stay informed with the latest IT news, security updates and product changes.

KB5097149 patches three CVEs in .NET 8.0: serialization RCE, ASP.NET Core DoS, and cryptographic info disclosure. Updates to version 8.0.28 on Windows, Linux, and macOS. No known issues.

Microsoft's June 2026 security update KB5094125 patches five vulnerabilities in Windows Server 2025, including a critical unauthenticated Remote Desktop Services RCE (CVE-2026-0235) and a Hyper-V guest-to-host escape (CVE-2026-0237). The update raises the OS build to 26100.32995 and applies to all editions across full GUI and Server Core installations.

Microsoft released KB5094122, the June 2026 cumulative security update for Windows 10 Version 1607 and Windows Server 2016, addressing critical remote code execution and privilege escalation vulnerabilities. The update moves the build to 14393.9234 and fixes flaws in the Windows Kernel, CLFS Driver, Graphics Component and Print Spooler.

Microsoft's June 2026 Patch Tuesday update KB5094123 addresses five CVE-tracked vulnerabilities in Windows 10 Version 1809 and Windows Server 2019, including a critical Windows kernel remote code execution flaw (CVE-2026-26001, CVSS 8.8). The update raises the OS build to 17763.8880.

Microsoft released KB5094041 on June 9, 2026, the monthly rollup for Windows Server 2012 R2 ESU systems. It patches kernel security flaws, fixes TLS 1.3 compatibility, resolves WMI memory leaks, and improves AD replication stability.

Microsoft's June 2026 security update KB5094128 patches multiple critical vulnerabilities in Windows Server 2022, including an unauthenticated NFS remote code execution flaw (CVE-2026-26001, CVSS 9.8), a Task Scheduler privilege escalation bug, an AD CS authentication bypass, and a Windows kernel memory corruption issue. The update raises the OS build to 20348.5256 and requires a restart.

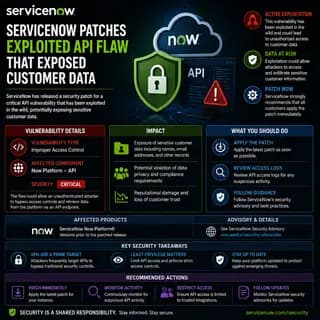
ServiceNow patched a misconfigured API endpoint that allowed unauthenticated queries of customer instance data, and observed successful table queries for a subset of customers - but says the activity appears attributable to security researchers, with no evidence data was retained or misused.

ServiceNow patched an unauthenticated API flaw on June 5, 2026, after attackers queried customer instance tables. Affects Australia release. Third major vulnerability in eight months.

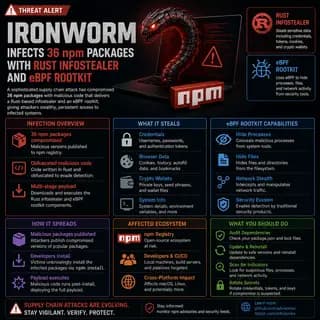
IronWorm is a Rust-based npm supply chain worm that infected 36 packages via the asteroiddao account. It steals credentials, deploys an eBPF rootkit, communicates over Tor, and self-propagates via stolen npm tokens.

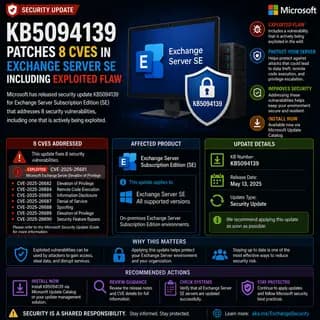
Microsoft’s June 2026 Exchange Server SE update KB5094139 addresses eight listed CVEs, including KEV-listed CVE-2026-42897. The fix for CVE-2026-45583 is not included and requires Microsoft’s separate mitigation guidance.

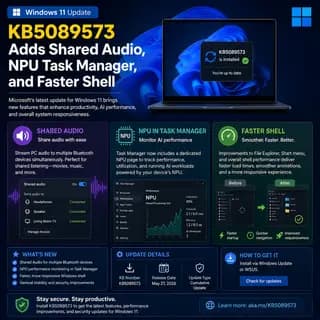
Microsoft released KB5089573 on May 26, 2026, an optional preview for Windows 11 24H2 and 25H2 (Builds 26100.8524/26200.8524) with Shared Audio, Task Manager NPU monitoring, Multi-App Camera, and shell performance gains under the K2 initiative.

Microsoft's KB5087051 cumulative update for .NET Framework 3.5 and 4.8.1 on Windows 11 Version 25H2 addresses four CVE-tracked vulnerabilities, including remote code execution, an ASP.NET Core authentication bypass, and a serialization denial-of-service flaw, alongside WCF stability and Entity Framework performance fixes.

Microsoft released KB5087054, a cumulative security update for .NET Framework 3.5 and 4.8.1 on Windows 11 Version 24H2 (x64). The update patches an elevation-of-privilege flaw in the CLR (CVE-2026-0234) and an ASP.NET request-validation bypass (CVE-2026-0235), alongside garbage-collector and reliability fixes. It requires a restart and carries several known post-install issues admins should test for.
Microsoft's May 2026 Patch Tuesday delivers KB5002866 for Office 2016, fixing CVE-2026-40358 (use-after-free) and CVE-2026-40363 (heap buffer overflow), both rated critical with CVSS 8.4.

KB5090408 patches CVE-2026-40370 (CVSS 8.8 RCE via path manipulation) in SQL Server 2019 GDR. Build 15.0.2170.1. For instances on the GDR servicing branch (no CUs). MSDASQL Msg 7416 breaking change. Superseded by KB5102336.

KB5087420 is the May 2026 Patch Tuesday update for Windows 11 23H2 (Build 22631.7079). Fixes the RDP multi-monitor warning issue from KB5082052, includes Secure Boot cert targeting improvements, and addresses BitLocker recovery behavior.

KB5087058 patches CVE-2026-32177 and CVE-2026-35433 (both .NET Framework EoP) on Windows 11 23H2. May 2026 Patch Tuesday security update for .NET Framework 3.5 and 4.8.1. No known issues.

KB5090407 patches CVE-2026-40370 (CVSS 8.8 RCE via path manipulation) in SQL Server 2019 CU32. Build 15.0.4470.1. MSDASQL linked server queries with @provstr fail with Msg 7416 after installation.